Digital Evidence in 2026: Collection, Preservation, Digital Forensics and Use in Criminal Investigations
Digital evidence is now part of far more investigations than traditional “computer crime” cases. A phone may record where a person travelled. A cloud account may show when a document was created. A vehicle may store location and infotainment records. A smart doorbell may capture an event outside a property. An online platform may retain account activity that never existed on the user's device. A cryptocurrency transaction may leave a permanent public trail even when the people behind the wallets are difficult to identify.

The problem for investigators is no longer simply finding electronic information.
The harder questions are:
Was the information collected lawfully? Is it authentic? Has it changed? Who handled it? Does the timestamp mean what it appears to mean? Can the source be identified? Is the evidence complete, or is an important part of the digital story missing?
These questions explain why digital forensics has become such an important part of modern criminal investigation.
Digital evidence can be extremely powerful, but it can also be misunderstood very easily.
Key Takeaways
- Digital evidence can come from phones, cloud accounts, vehicles, smart devices, online platforms, networks and blockchain records.
- Authenticity, integrity, context, lawful collection and documented handling all affect reliability.
- Digital evidence is fragile and may change through normal device use, synchronization, remote access or system activity.
- Strong investigations follow a documented lifecycle from identification through reporting.
- Hash values support integrity but do not prove authorship, truthfulness or lawful collection.
- Evidence is strongest when several independent sources support the same conclusion.
What Is Digital Evidence?
Digital evidence is information stored, processed or transmitted in electronic form that may help prove or disprove a fact in an investigation or legal proceeding.
It may include something obvious, such as a text message or photograph.
It may also include less visible information such as:
- system logs
- metadata
- browser history
- IP records
- cloud activity
- GPS information
- application databases
- deleted files
- authentication records
- network traffic
- device identifiers
- cryptocurrency transaction records
The original article correctly treats digital evidence as different from ordinary physical evidence because it may be copied, altered, deleted or distributed across different systems without an obvious physical change. That distinction is even more important in 2026.
Much of today's useful evidence may never exist in one device at all.
Why Digital Evidence Matters in Modern Criminal Investigations
Almost every modern activity creates electronic traces.
People use digital systems to:
- communicate
- travel
- make payments
- access buildings
- store photographs
- manage businesses
- use social media
- navigate roads
- transfer money
- control smart devices
- access cloud services
This means electronic records can help answer questions such as:
- Who communicated with whom?
- When was an account accessed?
- Which device was used?
- Where was a device located?
- Was a file created, changed or deleted?
- Did money move between accounts?
- Was a person connected to a particular online account?
- Was a photograph authentic or manipulated?
- Did a computer connect to another system?
But digital evidence rarely answers these questions perfectly on its own.
A login record may identify a device or network connection without proving who was physically using it.
A location record may place a phone somewhere without necessarily proving that its owner was carrying it.
A message may exist without proving who typed it.
Digital evidence therefore becomes strongest when different sources support each other.
Personal Evidence, Physical Evidence and Digital Evidence
Traditional criminal investigations often distinguish between personal evidence and physical evidence.
Personal Evidence
Personal evidence comes from people.
It may include statements from:
- witnesses
- victims
- suspects
- experts
- other persons with relevant knowledge
Human evidence can explain context that technical records cannot.
At the same time, memory can be incomplete or influenced by stress, time and misunderstanding.
Physical Evidence
Physical evidence includes tangible objects connected with an event.
Examples include:
- documents
- weapons
- fingerprints
- clothing
- computers
- mobile devices
- storage media
A computer or smartphone may therefore be physical evidence as an object while simultaneously containing digital evidence inside it.
Digital Evidence
Digital evidence is the information itself.
That distinction matters.
A seized mobile phone is a physical object.
Its messages, application records, location data and deleted files are digital evidence.
The device and the data should not automatically be treated as the same thing.
Digital Forensics and Computer Forensics
Computer forensics traditionally focused on desktops, laptops, operating systems and storage media.
Digital forensics is now the broader and more accurate term because modern investigations may involve many different technologies.
The original article already recognized this wider distinction. By 2026, major areas include:
Computer Forensics
Desktops, laptops, file systems, operating systems and storage media.
Mobile Forensics
Smartphones, applications, mobile operating systems and device records.
Network Forensics
Traffic, connection records, firewalls and communication activity.
Cloud Forensics
Remote cloud services, online accounts, backups and provider records.
IoT Forensics
Wearables, smart-home devices, sensors and connected systems.
Vehicle Forensics
Infotainment, telematics, navigation and paired-device records.
Drone Forensics
Flight data, GPS, controller records, images and device identifiers.
Blockchain Analysis
Transaction tracing and wallet activity across blockchain networks.
Where Digital Evidence Can Be Found in 2026
Investigators can no longer assume the relevant evidence is inside the device found at the scene.
A single incident may leave traces across several places.
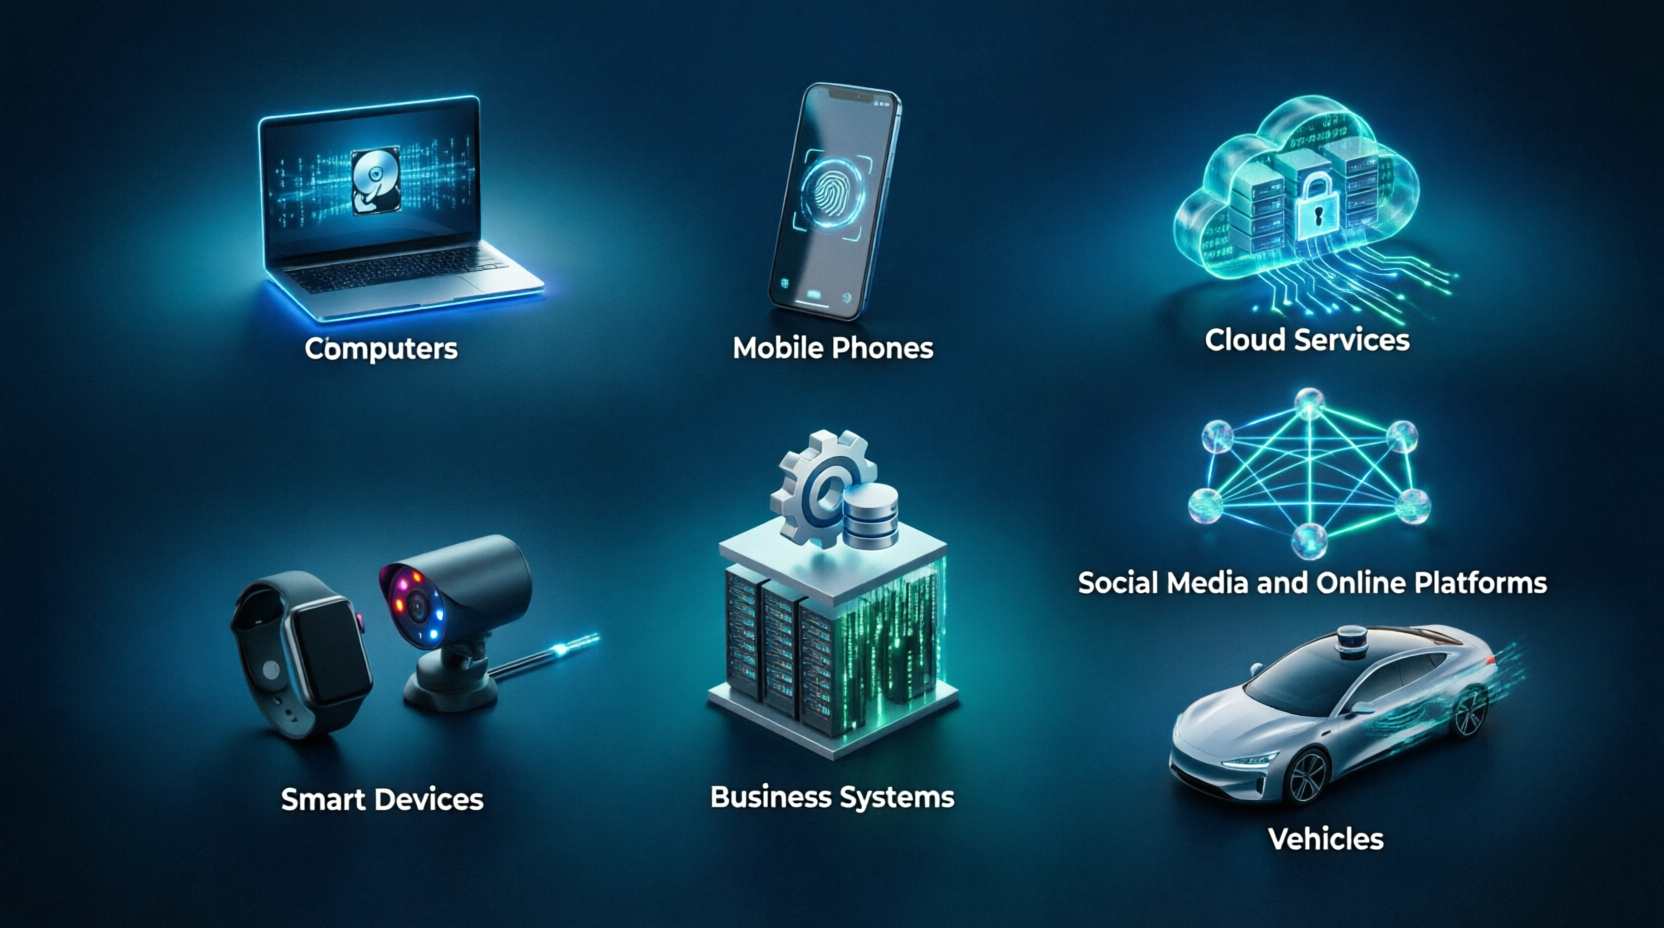
Computers
A computer may contain:
- files
- browser history
- operating-system logs
- downloads
- email records
- USB activity
- application data
Mobile Phones
Modern phones may contain:
- messages
- photographs
- call information
- app databases
- location history
- authentication records
- account tokens
- deleted data
Cloud Services
Important evidence may exist only on a service provider's systems.
Examples include:
- cloud backups
- file storage
- collaboration platforms
- account login history
- server-side messages
SWGDE now maintains specific best-practice guidance for acquisition, preservation and analysis of evidence from cloud service providers. SWGDE
Social Media and Online Platforms
Relevant information may include:
- public posts
- comments
- account names
- videos
- photographs
- timestamps
- profile changes
- URLs
SWGDE specifically recognizes acquisition and preservation of public-facing websites, streaming services and communication platforms as a separate digital-evidence problem. SWGDE
Smart Devices
A smart watch, security camera, doorbell, thermostat or voice assistant may contain information relevant to timing, activity or location.
Vehicles
Connected vehicles may store information about:
- destinations
- paired phones
- calls
- navigation history
- system events
Business Systems
Corporate investigations may depend on:
- access logs
- email servers
- databases
- employee devices
- security platforms
- cloud applications
Digital Evidence Is Fragile
One of the most important principles in the original article remains completely relevant in 2026.
Digital evidence can change simply because a device is used.
Opening a file can modify metadata.
Starting a computer may alter logs.
Connecting a phone to a network may trigger synchronization.
An application may automatically delete old data.
A remote user may wipe a device.
Cloud records may be overwritten according to retention schedules.
That is why evidence preservation should begin as early as possible.
INTERPOL's current guidance for first responders emphasizes that electronic data is intangible, volatile and easily altered, making preservation a central part of evidence handling. Interpol
The Digital Evidence Lifecycle
A reliable digital investigation is easier to understand when viewed as a sequence.
Identification
Identify devices, accounts, providers and other sources likely to contain relevant evidence.
Preservation
Prevent unnecessary alteration, loss or remote destruction.
Collection
Acquire evidence using methods appropriate to each source.
Examination
Locate messages, logs, files, timestamps and other relevant data.
Analysis
Interpret the evidence and compare it with other sources.
Reporting
Explain methods, findings, limitations and integrity checks clearly.

Preservation of the Original Evidence
Where technically appropriate, forensic analysis should be performed on an acquired copy rather than repeatedly examining the original source.
This protects the original evidence and makes the examination more reproducible.
The original article already emphasizes this principle. In practice, however, not every modern source can be handled in the same way.
A cloud platform cannot always be “imaged” like a hard drive.
A live system may need remote acquisition.
A smartphone may require specialized extraction.
Online content may need to be preserved before it changes or disappears.
This is why digital evidence procedures must be source-specific rather than based on one universal technique.
What Is a Forensic Image?
A forensic image is a controlled copy created for examination.
For storage media, the aim is generally to preserve the available data in a way that can later be verified.
The examiner should record:
- source device
- acquisition method
- date and time
- tool used
- operator
- integrity information
A normal file copy is not always equivalent to a forensic acquisition because ordinary copying may omit deleted information, system areas or metadata.
Hash Values and Evidence Integrity
Hashing is one of the best-known integrity checks in digital forensics.
A cryptographic hash produces a value calculated from the data.
If the data changes, the resulting hash should normally change as well.
Hashes can therefore help demonstrate that a forensic image or file remained unchanged between stages of handling.
But a hash does not prove everything.
It does not prove:
- who created the file
- whether its contents are true
- whether it was collected lawfully
- whether the original source itself was authentic
Hashing supports integrity.
It does not replace authentication and contextual analysis.
Chain of Custody
Chain of custody records who handled evidence and what happened to it from collection to presentation. For practical documentation, you can also use our chain of custody report generator.
A proper record may include:
- evidence identifier
- date and time
- person collecting it
- transfers between personnel
- storage location
- examination activity
- return or release
Digital evidence should be traceable throughout its lifecycle.
A missing chain-of-custody entry does not necessarily mean the data changed, but unexplained gaps may create questions about reliability.
Volatile Evidence
Some electronic information may disappear when a system is shut down.
Examples can include:
- running processes
- active network connections
- volatile memory
- encryption keys
- temporary session information
This creates an important decision for investigators.
Turning a computer off may preserve some information while destroying other information held only in memory.
Keeping it running may preserve volatile information but allow the system to continue changing.
There is no single correct rule for every situation.
The response should depend on the technical circumstances and the investigator's training.
Mobile Device Evidence
Mobile phones are now among the richest sources of digital evidence.
They can contain information from many parts of a person's life.
Relevant material may include:
- messages
- call records
- photographs
- videos
- applications
- location information
- browser activity
- authentication records
Mobile evidence also creates special challenges.
Phones are constantly changing.
They communicate with cloud services.
Applications use encryption.
Remote wiping may be possible.
Operating-system security may restrict acquisition.
SWGDE released updated mobile evidence collection, preservation and acquisition guidance in 2025, reflecting the continuing technical complexity of this area. SWGDE
Cloud Evidence
Cloud computing has changed one of the oldest assumptions in forensic investigation: that the evidence is located where the device is found.
A laptop may contain only a local reference to information actually stored in another country.
A cloud account may contain:
- files
- authentication logs
- account history
- backups
- messages
- collaboration records
Cloud investigations therefore raise questions about:
- provider cooperation
- legal authority
- jurisdiction
- account ownership
- retention periods
- timestamps
- multi-tenant infrastructure
Cloud evidence may also change rapidly.
Investigators should therefore consider preservation early.
Online and Social Media Evidence
Screenshots can be useful, but they are not always the strongest way to preserve online evidence.
A screenshot may fail to record:
- URL
- source information
- metadata
- surrounding page context
- embedded content
- time of capture
Better preservation may involve recording the complete page, URL and contextual information.
SWGDE guidance on acquiring online content stresses relevance, reliability and sufficiency, and the examiner should be able to explain how the content was discovered and preserved. SWGDE
Internet of Things Evidence
Connected devices now create evidence that earlier investigations would never have considered.
Examples include:
- smart doorbells
- security cameras
- fitness trackers
- smart speakers
- home automation systems
- connected appliances
The difficult question is often not whether the device exists, but where its data is stored.
Some data may be:
- on the device
- on a mobile application
- in the cloud
- on the manufacturer's servers
An IoT investigation may therefore require several different collection methods.
Vehicle and Telematics Evidence
Modern vehicles are increasingly digital systems.
Relevant evidence can include:
- navigation destinations
- paired device information
- communication history
- system events
- telematics records
This can assist investigations involving movement, timing or device association.
SWGDE's current forensic guidance specifically includes vehicle infotainment and telematics systems. SWGDE
Drone Evidence
Drones may store:
- GPS information
- flight routes
- photographs
- videos
- controller records
- device identifiers
The evidence may exist across the aircraft, controller, mobile application and cloud account.
Drone evidence has become sufficiently common that SWGDE maintains dedicated forensic guidance for it. SWGDE
Cryptocurrency and Blockchain Evidence
Cryptocurrency investigations illustrate an important digital-forensics principle.
Transactions can be publicly visible without making the identity behind them obvious.
Blockchain analysis may help trace movement between addresses.
But investigators often need additional evidence to connect a wallet to a person.
That may come from:
- exchange records
- seized devices
- messages
- account records
- financial documents
Technical tracing and attribution should not be treated as the same thing.
AI-Generated and Manipulated Digital Evidence
By 2026, investigators also have to consider whether digital media has been generated or manipulated using artificial intelligence.
Photographs, voices and videos may now be altered convincingly.
This means visual appearance alone may not establish authenticity.
Investigation may require examination of:
- source files
- metadata
- compression history
- editing traces
- provenance records
- surrounding contextual evidence
SWGDE's recent forensic guidance includes updated work on image authentication and forensic image analysis, reflecting the growing importance of verifying digital media rather than accepting it at face value. SWGDE

Deleted Digital Evidence
Deleting a file does not always mean the information immediately disappears.
Depending on the system, deleted information may remain recoverable until the underlying storage is overwritten.
Recovery depends on factors including:
- device type
- file system
- encryption
- storage technology
- later device use
Modern solid-state storage and mobile encryption can make recovery more difficult than older computer-forensics assumptions suggest.
For this reason, investigators should not promise that deleted information can always be restored.
Metadata as Evidence
Metadata is information about other data.
It may show:
- creation time
- modification time
- author
- device
- location
- application
- file properties
Metadata can be extremely useful.
It can also be misunderstood.
A timestamp may be affected by:
- time-zone settings
- synchronization
- copying
- software behaviour
- device configuration
Metadata should therefore be interpreted in context rather than treated as an unquestionable fact.
Digital Traces and Attribution
Digital systems leave traces when they communicate.
These may include:
- IP addresses
- account identifiers
- cookies
- device IDs
- authentication logs
- network records
These traces can help connect events.
But connection is not always attribution.
An IP address may identify a network connection rather than a specific individual.
A registered account may be used by another person.
A shared device may have several users.
Reliable attribution often requires several independent pieces of evidence.
Authentication of Digital Evidence
Before electronic material can be trusted, the party relying on it may need to show that it is what it claims to be.
Authentication may involve:
- witness testimony
- device records
- provider records
- metadata
- hash values
- forensic analysis
- account information
- surrounding circumstances
Different jurisdictions use different evidentiary rules, but authenticity remains a central issue internationally.
Admissibility of Digital Evidence
There is no single worldwide rule for admissibility.
Each legal system has its own evidence law and procedural requirements.
INTERPOL's digital-forensics laboratory guidance identifies several broad considerations commonly relevant to electronic evidence, including authenticity, completeness, reliability, persuasiveness and proportionality. Interpol
In practical terms, courts may ask:
- Is the evidence relevant?
- Is it authentic?
- Was it collected lawfully?
- Was its integrity preserved?
- Can the forensic method be explained?
- Is the examiner qualified?
- Are important limitations disclosed?
The Importance of Completeness
A technically authentic file can still create a misleading picture if important surrounding evidence is missing.
For example, one message may appear threatening when viewed alone but take on a different meaning when the entire conversation is examined.
A forensic examiner should not select only evidence that supports one theory.
Completeness does not necessarily mean collecting every file in existence.
It means presenting enough reliable context to avoid creating a distorted conclusion.
Focused Collection and Data Minimization
Modern investigations often involve enormous quantities of private information.
A smartphone may contain years of photographs, messages and location history.
A cloud account may contain far more information than the investigation requires.
Forensic practice is therefore moving increasingly toward focused collection where technically and legally appropriate.
SWGDE's current publications specifically include guidance on focused collection and minimization of digital evidence seizure. SWGDE
This serves both practical and privacy interests.
Legal Authority and Privacy
Technical ability does not automatically create legal authority.
Investigators may be capable of accessing large amounts of information but still require lawful authorization.
Depending on the jurisdiction, obtaining digital evidence may involve:
- consent
- search warrants
- court orders
- subpoenas
- statutory powers
- provider disclosure procedures
Privacy should remain part of forensic decision-making.
The original article correctly stresses that cybercrime investigation must be balanced against individual rights. That principle remains essential.
Cross-Border Digital Evidence
Cloud computing has made international evidence problems much more common.
A suspect may be located in one country.
The victim may be in another.
The service provider may be headquartered in a third.
The relevant server may be somewhere else entirely.
This raises difficult questions about:
- jurisdiction
- provider disclosure
- preservation
- mutual legal assistance
- data protection
- conflicting national laws
ISO 27037 specifically recognizes the importance of procedures that facilitate exchange of potential digital evidence between jurisdictions. ISO
Digital Forensics First Responders
The first person who encounters electronic evidence can affect everything that follows.
A poorly trained responder may:
- switch on a device unnecessarily
- alter files
- connect equipment to a network
- fail to document connections
- lose volatile evidence
- break the chain of custody
INTERPOL's recent guidance focuses specifically on first responders because early search, seizure and preservation decisions can directly affect whether electronic evidence remains useful later. Interpol
Role of the Digital Forensic Examiner
A competent examiner does more than operate forensic software.
The examiner should understand:
- operating systems
- storage technology
- acquisition methods
- application data
- forensic limitations
- legal requirements
- documentation
- reporting
The examiner should also be willing to explain what the evidence cannot prove.
That is often as important as explaining what it can prove.
Forensic Tools Do Not Replace Expertise
digital forensic tools can process enormous amounts of information.
It can recover files, parse databases and organize communications.
But software output still needs interpretation.
A tool can identify a timestamp.
An examiner must determine what that timestamp actually represents.
A tool can recover a message.
An examiner must determine whether its context and source can be authenticated.
Forensic software should therefore assist professional judgment rather than replace it.
Reporting Digital Evidence
A forensic report should be understandable to someone who is not a computer scientist.
It should normally explain:
- what evidence was received
- what was examined
- methods used
- tools used
- significant findings
- limitations
- integrity checks
- conclusions
INTERPOL recommends presenting technical findings in a way that judges, prosecutors and other stakeholders can understand. Interpol
A technically perfect investigation can lose much of its value if nobody can understand the report.
Common Mistakes in Digital Evidence Investigations
Several mistakes appear repeatedly.
Examining the original unnecessarily
This can alter data.
Relying only on screenshots
Screenshots may lack context or technical information.
Ignoring cloud evidence
Important records may exist outside the device.
Treating IP addresses as proof of identity
They may prove a connection rather than a person.
Assuming timestamps are always correct
System settings and software behaviour can affect them.
Collecting too much data
Over-collection can create legal, privacy and analytical problems.
Failing to record forensic limitations
Courts should understand what the examination could and could not establish.
Trusting AI-generated or edited media without verification
Modern digital content requires stronger authentication than visual appearance alone.
What Makes Digital Evidence Reliable?
Reliable digital evidence usually depends on several things working together.
It should be:
Relevant
It must help answer a question that actually matters to the case.
Authentic
There should be a reasonable basis for believing the evidence is what it claims to be.
Preserved
Unnecessary alteration should be prevented.
Documented
The handling and examination process should be recorded.
Reproducible
Another qualified examiner should, where possible, be able to understand and test the process.
Complete Enough
The evidence should not be presented in a misleading way by removing important context.
Digital Evidence and the Courtroom
The courtroom is where technical work must become understandable evidence.
Lawyers and judges do not necessarily need to know how every forensic tool works internally.
They do need to understand enough to ask the right questions.
For example:
- Where did the evidence come from?
- Who collected it?
- Was it altered?
- What does the timestamp actually mean?
- Is the account linked to the person or merely registered in their name?
- Could another person have used the device?
- What assumptions did the examiner make?
- Were alternative explanations considered?
Good digital forensics should survive these questions.
Frequently Asked Questions
Digital evidence is electronically stored, processed or transmitted information that may help establish a fact in an investigation or legal proceeding.
Examples include messages, emails, photographs, videos, system logs, metadata, cloud records, location information, application data and network records.
Yes, it can be evidence, but a screenshot may not preserve all available technical or contextual information.
Digital forensics is the process of identifying, preserving, acquiring, examining, analysing and presenting electronic information for investigative or legal purposes.
Computer forensics focuses mainly on computers and computer storage. Digital forensics is broader and includes mobile devices, cloud services, networks, IoT systems, vehicles and other electronic sources.
Electronic information may change through ordinary system activity, deletion, synchronization, remote access or improper handling.
A forensic image is a controlled copy of electronic storage created for examination while helping protect the original evidence.
A hash can help show whether the data being checked has changed. It does not prove that the content is true or identify who created it.
Chain of custody is the documented history showing who collected, handled, stored and examined evidence.
Sometimes. Recovery depends on the device, storage technology, encryption and whether the underlying data has been overwritten.
Yes. Cloud platforms may contain files, messages, authentication records, backups and account history relevant to an investigation.
Potentially, yes, but authenticity, preservation, context and the applicable evidentiary rules must still be considered.
An IP address can help establish a network connection, but it should not automatically be treated as proof that a particular individual carried out the activity.
They can become relevant evidence, but modern synthetic and manipulated media require careful authentication and contextual examination.
The rules vary by jurisdiction. There is no single international admissibility rule.
An expert can explain the acquisition method, technical findings, limitations and significance of electronic evidence to the court.
Digital Evidence in 2026
Digital evidence in 2026 encompasses a variety of sources beyond just desktop files, including smartphones, cloud accounts, online platforms, smart devices, and more. This broad range enhances the utility of digital evidence but also complicates its management. Key principles remain unchanged: evidence must be identified, preserved, collected using defensible methods, and documented throughout its lifecycle.
Need Help Understanding Digital Evidence?
Digital evidence can be powerful, but its value depends on lawful collection, preservation, authentication, context and clear forensic explanation.
Contact Qanooni Rah